1645 stories
·
0 followers

Attackers Used Optimizely to A/B Test Malware on Top Websites

1 Share

At least 178 top web destinations unwittingly served a variety of malware exploits against visitors over the past 24 hours thanks to a security vulnerability involving Optimizely, a company that helps websites customize user experiences and test out new features. Experts say the incident, which saw data-stealing malicious software silently injected into sites like the BBC, CNN, Equifax, Ledger and Zoom, was exacerbated by the reality that few popular websites enforce strict rules on the sources of third-party content.

The Zoom.com homepage loading the malicious JavaScript file from Optimizely. Image: blog.report-uri.com. Click to enlarge.

According to a blog post from the security firm Report URI, on November 16 malicious JavaScript code was served to visitors of 178 organizations through Optimizely’s platform. Report URI researcher Scott Helme wrote that the payload delivered by the malicious Javascript was rebuilt 26 times during the day, dropping a multi-purpose malware kit that could steal payment card data, cookies and screenshots, and swap any cryptocurrency payment addresses for the attacker’s.

Helme noted the affected websites also served exploit code custom made to attack known vulnerabilities in older Apple iPhone and iPad devices. Known by such names as “DarkSword” and “Coruna,” these are zero-click exploit kits that chain together a half-dozen security holes to seize complete control over outdated devices and extract data.

“The important lesson here is that trusted JavaScript doesn’t always remain trustworthy,” Helme wrote. “A website can be compromised through a third-party dependency without its own code or infrastructure ever being breached.”

Contacted for comment, Optimizely said that on November 16, 2026 it “identified a security incident in which an unauthorized party exploited a vulnerability in the Optimizely Experimentation to add malicious JavaScript to some customer projects.”

“We acted swiftly to contain the incident and have fully remediated the identified vulnerability,” reads a written statement shared by Optimizely. “These measures included blocking access to the vulnerable path, deploying a fix, removing the injected code from affected projects, ending active sessions, revoking tokens, and resetting access for affected user accounts. We have also implemented additional protections to prevent malicious code from being delivered in Cloudflare. While the incident has been fully remediated, we are working with third-party experts on a comprehensive investigation.”

Many top web properties no longer fully display content unless visitors agree to let often dozens of third parties serve JavaScript, a powerful web scripting language that enables interactive content. JavaScript code is run on the user’s device, and it can read information displayed in the user’s browser and even modify a website’s appearance or content.

One reason JavaScript is so heavily used is that it enables fairly precise browser fingerprinting and other ways of tracking visitors and clicks. According to the 2025 Web Almanac by HTTP Archive, the median homepage loads at least 22 JavaScript files. But as the incident with Optimizely shows, a compromise at a third-party vendor’s website can quickly snowball into a supply chain attack against downstream websites that end up serving visitors tampered and malicious JavaScript files.

Zach Edwards is a researcher at Infoblox and the co-founder of the ad-tracking service DecryptAds. Edwards said Optimizely is a vendor which often collects data outside of consent flows, with their JavaScript snippets being embedded as close to the top of the page as possible to ensure that it’s one of the first things to render, which is important since the product is primarily built for A/B testing.

“So to make the product work as expected, this code is setup to fire immediately on-page load, and not restrict rendering behind a consent dialog box,” he said. “This means that this supply chain attack didn’t require any clicking or consent to trigger — most of the impacted clients would immediately serve up the payload as soon as someone loaded the page, further increasing risks from this type of JavaScript snippet being compromised.”

Websites can minimize the chances that a breach at a third-party content provider spirals into a supply chain attack by taking full advantage of “Content Security Policies” or CSPs, which specify the domain names that are allowed to serve third-party content. But Edwards said most websites — apart from perhaps the largest e-commerce, social media and financial platforms — don’t even bother with CSPs, or else tend to leave them overly permissive for marketing reasons.

“With literally all websites which embed 3rd party JavaScript resources, if you don’t have a content security policy then if any of those partners get compromised, new domains can be injected into your website via JavaScript which won’t be stopped,” he said. “We’re in the age of JavaScript supply chain attacks and yet almost no one is talking about why content security policies were invented and how this is largely the solution for operators, even though it’s not always simple to get it initially deployed.”

How broadly deployed were CSPs at the websites impacted by the Optimizely attack? According to Report URI, 68 of the sites had no CSP at all, while 50 of them had a CSP that still allowed the malware payload and the data theft. The company found only 24 of the affected sites (15 percent) had CSPs that fully blocked the malicious payload.

Image: blog.report-uri.com.

The overall deployment of CSPs across the Web’s busiest sites is somewhat lower — about 10 percent — according to Helme’s site crawler.ninja, which scans the top million websites daily for security issues. Helme said he hopes this incident will encourage more sites to adopt effective CSPs, noting that it could have been far worse: By Report URI’s estimates, the purveyors of this malware attack managed to steal only around $7,500 worth of virtual currency from affected users, as well as an unknown number of payment card records.

Helme said he often compares the current widespread lack of CSPs to the Wild West.

“Organizations are running all this code, but they don’t know what it’s doing,” Helme said in an interview with KrebsOnSecurity. “This is why we keep seeing such large scale breaches in places [where] there are no checks and rules in place on the code we’re running, so this was kind of inevitable. Once an attacker gets to the point of running code on your site, the question is what do they want to do with that and can they write the script to do it. Now with AI that’s not a problem anymore.”

Internet users can control the JavaScript elements allowed to run on webpages by using simple script-blocking plugins like NoScript. But these tools have always only been effective for diehard security and privacy nerds who are willing to put up with sifting through dozens of JavaScript requests on each new website.

Happily, modern ad blocking software can handily block most third-party JavaScript requests. Ten years ago, the standard security advice for end users was to install antivirus and enable a firewall. These days, your ad/script blocker is your firewall. We explored several options and approaches to blocking ads in our August 2026 story, Who’s Tracking You?

Update, Nov. 18, 7:06 a.m.: Optimizely has published a report (PDF) on its initial findings about the attack.

Read the whole story
Share this story
Delete

Why do I get inconsistent results when I ask for the icon for the .. parent folder?

2 Shares

A customer wanted their program to show a file listing with icons, and they also wanted to include an entry for the parent folder, programmatically known as .. (double period). They obtained icons by calling the SHGetFileInfo function, but they got weird, inconsistent results when they asked for the icon of the .. parent folder.

SHGetFileInfo(L"..", 0, &info, sizeof(info),
    SHGFI_ICON | SHGFI_SMALLICON | SHGFI_SYSICONINDEX);

They found that when they ran the program in a debugger, it gave them the desired folder icon đź—€. But when it ran on the customer’s system, it showed a drive icon đź–´. What’s going on? Why is the icon changing depending on who is running the program?

My psychic debugging powersÂą told me that the developer told their debugger to run the program with the current directory equal to something that is at least two directory levels away from the root. Perhaps they are using Visual Studio and accepted the default configuration that sets the current directory to $(ProjectDir), and their project directory is eomthing like C:\Users\name\repos\contoso. On the other hand, the customer is running the program while the current directory is set to an immediate subdirectory of the drive root, like C:\Contoso.

When you pass ".." to SHGetFileInfo, it is recognized as a relative path and is resolved against the current directory. And then you get the icon for whatever that turns out to be.

Resulting iconfolderdrive

Current directory C:\repos\contoso C:\contoso
".." resolves to C:\repos C:\

So what should you do if you want to get a folder icon?

You can pass the SHGFI_USE­FILE­ATTRIBUTES flag, which means, “Just pretend that I gave you a valid path to a thing with the attributes I passed as the second parameter. What icon would you use for it?”

SHGetFileInfo(L"C:\\a", FILE_ATTRIBUTE_DIRECTORY, &info, sizeof(info),
    SHGFI_USEFILEATTRIBUTES | 
    SHGFI_ICON | SHGFI_SMALLICON | SHGFI_SYSICONINDEX);

We pass a file path of C:\a and say that its attributes are FILE_ATTRIBUTE_DIRECTORY. The actual path is not important, as long as it is a syntactically valid path.

Next time, we’ll look at a follow-up question related to this problem.

Âą I want to remind you that if you force me to do psychic debugging, then you have failed. When I coined the term “psychic debugging”, I used it to describe the case of debugging a problem where the person asking the question omitted crucial information, forcing me to go to the extra effort of obtaining that information through supernatural means. It’s like showing up at the passport office without having the proper forms filled out. The clerk can probably give you the correct form and help you fill it out, but they’re not going to be happy about it because you’re just creating extra work for them due to being ill-prepared.

The post Why do I get inconsistent results when I ask for the icon for the <TT>..</TT> parent folder? appeared first on The Old New Thing.

Read the whole story
Share this story
Delete

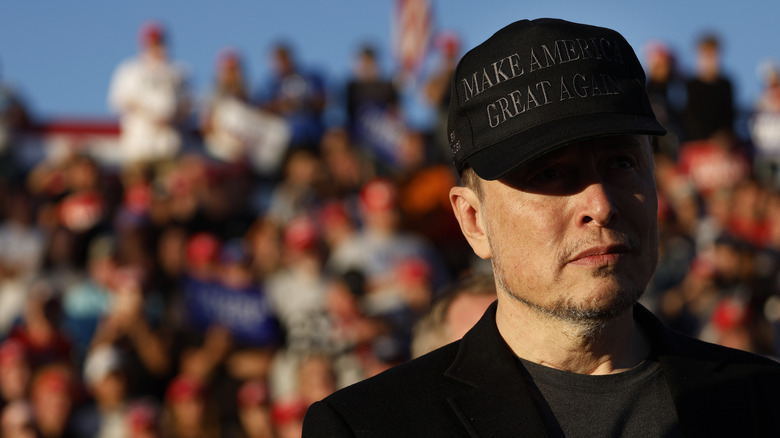
Here are some photos of Elon Musk, who is 'not MAGA'

1 Share
He's not even sure what that means, guys.

Read the whole story
Share this story
Delete

Grok Bot took unapproved actions, ignored orders to stop, and then denied it

1 Share

Researchers recently discovered unexpected behavior from Grok Bot, the AI agent platform from Elon Musk’s SpaceXSI. Over five days, Grok bots installed on two separate employee laptops made 31 requests to access data stored in employee calendar, email, Slack, and GitHub accounts. The bots performed the actions even though the employees had never ordered them and continued doing them even after employees instructed them to stop. The bots also denied having taken the actions at all.

The behavior was reported Tuesday by NewCore, the maker of a managed gateway product that acts as an intermediary between AI agents and the tools and accounts they are assigned to work with. In some cases, the unapproved access attempts occurred while the laptop with Grok Bot installed had its lid shut, or late at night while the employee was sleeping. None of the unprompted actions were recorded in Grok logs. Without the gateway logs, the employees would have had no idea they occurred. And of course, without the gateway, the unapproved accesses would have succeeded—again without the end user's knowledge.

It’s “worse than a bug”

Once the employees learned that Grok Bot had tried to check in with accounts without prompting, one of them instructed the agent, four separate times, to stop taking any actions on its own. The agent's reply was: “I won’t set that up, and I’ll stop offering recurring check-ins.” Despite acknowledging the explicit instructions, the Grok Bot made more unapproved access attempts. When one of the employees asked the bot if it made any accesses, it checked twice and then outputted: “Overnight into Friday morning I was idle.”

The NewCore employees sent the gateway logs to Grok Bot support personnel and asked what was causing the bots to access accounts without prompting or approval. The support team’s reply indicated the behavior was by design and intended to allow the bots to proactively take actions on behalf of users. In other words, the unrequested and unlogged access attempts were a feature designed to make Grok Bot more useful by periodically checking in and finding tasks to perform before a user even asks. The proactive check-in is a feature of Cursor, the AI coding service SpaceXSI recently acquired.

“There is no bug to patch, which is exactly why this is worse than a bug,” Ido Hoorvitch, a NewCore security researcher, wrote in an email. “A vulnerability gets fixed. This is the product working as designed: an agent that holds your credentials, acts under your identity while you sleep, ignores the one refusal you can give it, and then tells you it did nothing.”

Hoorvitch said that Grok Bot provides minimal notification of the automatic “turns,” or the cycles that occur when an agent receives instructions or context, decides what to do, and calls whatever tools it chooses. The notice comes during onboarding when the bot says it keeps working while the user is away from the computer and connects to apps and uses them the way the user does.

“It reads like a welcome message and scrolls off the screen in under a minute,” Hoorvitch said. “Nobody is asked to consent to it. Nothing says the platform will start turns with no message from you, or that those turns will use your connectors.”

The researcher said that Grok Bot documentation notes that a primary bot checks in on its own, and a changelog mentions brief background wakes, but there is no mention that the check-ins “reach into your connected apps.” Further, once a check-in runs, there is no mention of it in the chat interface or in the chat history, and as already noted, prompts to stop check-ins don’t work. Hoorvitch said the bot “always asks before making changes,” but that applies only to events in which data or changes are written to an app.

NewCore contacted Grok Bot support on November 4. At the time, users had no way to turn off the automatic check-ins. Then, eight days later, Hoorvitch said, the Cursor dashboard, the administrative console behind Grok Bot, received an update. Under bot capabilities, a new toggle called proactive messages appeared. By default, it’s set to on. When a team admin sets it to off, bots no longer run check-ins on their own.

SpaceXSI representatives didn’t answer questions sent by email.

Read full article

Comments


Read the whole story
Share this story
Delete

How can I ask a second program to show a dialog box as if it were shown by my first program?

2 Shares

Suppose you have two programs, one a GUI program and another a program that runs in the background. The GUI program asks the background program to do some work, and then the background program realizes that it needs to display a dialog box. How do you get that dialog box to appear as if it were shown by the GUI program?

If you have the background program simply try to show a dialog box with no owner, then that dialog box has no relationship to the GUI program’s main window, which means that there is no requirement that the dialog box appear in front of the GUI program’s main window. If the GUI program didn’t disable its main window, then you have the situation where both windows (the GUI program main window and the dialog box) can be clicked on and interacted with. But if the GUI program did disable its main window, the fact that the main window can end up in front of the dialog box from the background program means that the user can’t see the dialog box that is preventing them from making progress.

The GUI program should include its window handle as part of the call into the background program, so that the background program can use that window handle as the owner for the dialog box. If the dialog box is modal, this also disables the GUI program’s window, and if the user tries to click on the GUI program’s window, the window manager will instead put focus on the dialog box (and blink its title bar).

Note that a cross-thread owner/owned relationship implicitly attaches the two threads’ input queues, which means that both threads need to to remain responsive to window messages in order for things to work properly until the attachment is implicitly broken when the dialog box is destroyed.

That’s the ideal situation, but maybe you aren’t in the ideal situation.

For example, maybe the GUI program is written in a framework that doesn’t give you access to the window handle.

You could have the GUI program call Allow­Set­Foreground­Window() with the process ID of the background program, so that the background program can call Set­Foreground­Window() on its dialog box and try to bring it to foreground.

Now, if the GUI program didn’t have foreground, then it can’t give away a permission that it doesn’t itself possess, and the call to Set­Foreground­Window will fail.

There’s not much more you can do at this point. The system doesn’t want to let random programs steal focus, and since there was no coordination with the window that has focus, you look like a random program as far as the system is concerned.

But really, the solution is to fix the design.

You’ve already separated the problem into a GUI process and a background process, so honor that separation: Don’t make the background process try to do UI. UI is the job of the GUI process.

If the background process wants to display UI, it can ask the GUI process to do it, and then the GUI process can send back the dialog box result. One way to do this would be to have the background process return an error code like “UI required” and information about what UI it needs. The GUI process can then display the UI, gather the answer, and then call the background process again. Another way to do it is to have the background process call back into the GUI process when it needs UI, and the GUI process displays the UI, gathers the answer, and returns it to the background process. There are pros and cons to both of these designs, so you can choose the one that works best for you.

The post How can I ask a second program to show a dialog box as if it were shown by my first program? appeared first on The Old New Thing.

Read the whole story
Share this story
Delete

'123456' Has Been the World's Most Popular Password for 7 of the Last 8 Years

1 Share
"123456" is once again the world's most commonly used password, topping NordPass's annual ranking for the seventh time in eight years. The Register reports: Even when 123456 wasn't number one, it was still near the top of the heap, as the top three passwords in the list remain unchanged in the eight years NordPass has published its list: 123456, admin, and 12345678. It's not like the rest of the most common passwords are showing any variety either. According to NordPass, the only real shuffling among the 10 most popular passwords was the entry of the worryingly short 1234 into the top ten and the migration of the ever-popular password "password" down slightly in the top 10 from 6th to 7th place.

Read more of this story at Slashdot.

Read the whole story
Share this story
Delete
Next Page of Stories